Next-Generation Third-Party Risk Management Platform
CompliScan is engineered by JE3.COM to deliver continuous visibility and automated governance over your entire vendor ecosystem. Unify supplier onboarding, risk analytics, 4th-party cascade mapping, and auditor-ready compliance in one continuous platform.
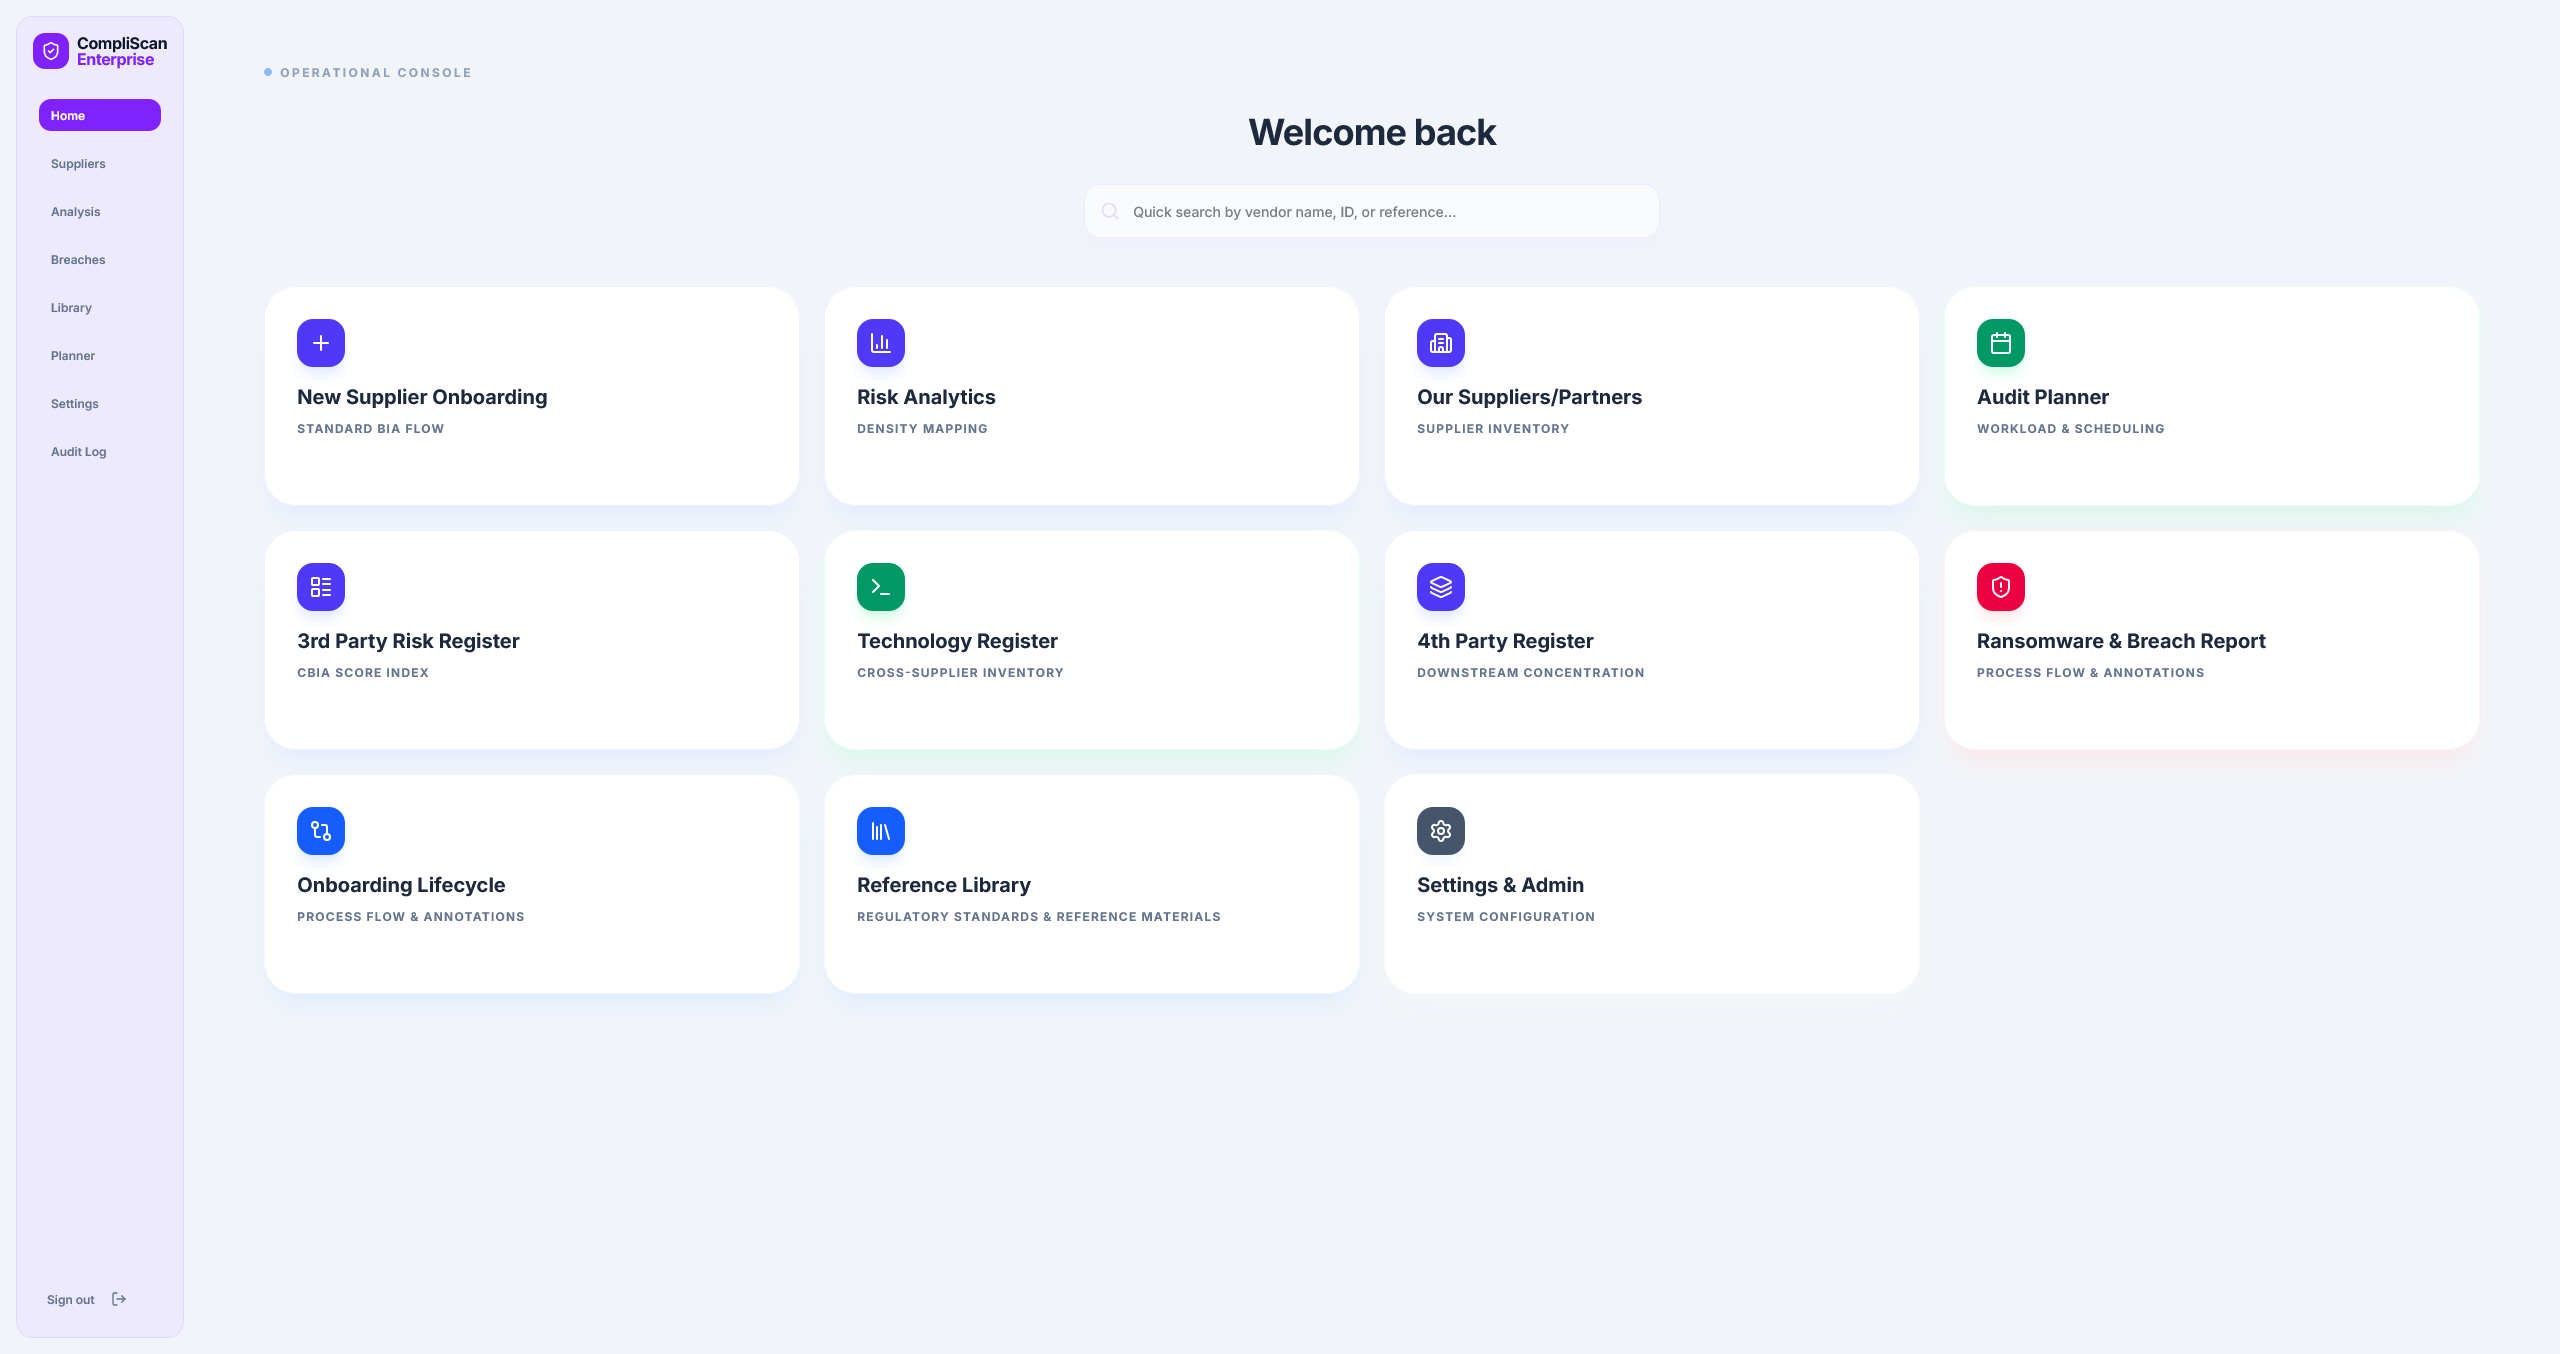
Complete TPRM Governance Suite
Every capability required to discover, assess, continuously monitor, and audit third and fourth-party vendors with zero blind spots.
Supplier Onboarding
Streamlined vendor intake workflows with customizable security intake questionnaires, automated risk-tier scoping, and rapid supplier evaluation pipelines.
Risk Analytics
Quantitative scoring algorithms combining continuous OSINT data, compliance postures, and financial stability metrics into actionable risk telemetry.
Supplier Inventory
Centralized repository for every vendor, service provider, and external contractor with contract terms, data access tiers, and operational criticality tags.
Audit Planner
Automated recurring vendor assessment scheduling, automated reminder sequences, stakeholder task assignment, and reassessment triggers.
3rd Party Risk Register
Comprehensive risk log documenting identified vulnerabilities, residual risk ratings, treatment plans, executive sign-offs, and mitigation tracking.
Technology Register
Catalog and profile of all SaaS, IaaS, software libraries, and digital tools utilized across vendors to detect end-of-life frameworks and CVE vulnerabilities.
4th Party Register
Map hidden downstream dependencies, subcontracted cloud hosts, sub-processors, and critical shared infrastructure to prevent systemic cascading failure.
Ransomware & Reach Reports
Proactive threat impact modeling calculating your organization's exposure radius if a key supplier or their cloud dependency suffers a ransomware breach.
Onboarding Lifecycle
End-to-end lifecycle orchestration from initial intake, NDA signing, security vetting, risk mitigation, to recurring reassessment and contract offboarding.
Reference Library
Curated repository of standardized security clauses, questionnaire templates (SIG, CAIQ, VSA), remediation playbooks, and best practice policies.
Compliance Management
Multi-regulation cross-mapping engine ensuring suppliers satisfy GDPR, HIPAA, DORA, PCI-DSS, NIS2, and SEC third-party cybersecurity disclosure rules.
BIA (Business Impact Analysis)
Rigorous evaluation of vendor dependencies against RTO (Recovery Time Objective) and RPO (Recovery Point Objective) metrics for mission-critical operations.
Relationship Profiles
Holistic 360-degree dossiers documenting vendor key contacts, SLAs, contract values, executive sponsors, and historical security performance.
Standards Benchmark
Automated benchmark validation against international security controls: ISO 27001, SOC 2 Type II, NIST CSF 2.0, CIS Controls, and CSA STAR.
Auditors Pack
One-click generation of immutable, auditor-verified TPRM evidence bundles, risk acceptance justifications, and compliance verification packages.
Multi-Tier Registers & Impact Modeling
Moving beyond static spreadsheets with dynamic relational registers that track your vendors, their technical assets, and cascading downstream dependencies.
3rd & 4th Party Risk Registers
HIERARCHICAL RISK PROPAGATION
Map direct third-party suppliers and their critical sub-processors (4th-parties). When a sub-vendor suffers an outage or breach, CompliScan automatically calculates which of your primary contracts and business units are impacted.
Ransomware & Reach Reports
PROACTIVE EXPOSURE QUANTIFICATION
In the event of active zero-day exploits or ransomware outbreaks, instantly generate a blast-radius report revealing which vendors operate vulnerable technologies and what data they hold.
Relationship Profiles
Consolidate internal business owners, contract SLA thresholds, data residency boundaries, and vendor security contacts into a unified single dossier.
BIA (Business Impact Analysis)
Dynamically calculate operational, financial, and reputational risk severity if a service provider goes offline for 1 hour, 1 day, or 1 week.
Auditors Pack & Reference Library
Export complete documentation packages with pre-built questionnaire frameworks, compliance mappings, and cryptographically verified evidence.
Built-In Industry Integrations
CompliScan doesn't rely solely on self-reported vendor questionnaires. Automated OSINT feeds continuously validate vendor security posture against live internet telemetry.
Shodan
Surface Attack Analysis
Continuously scans vendor domains for open service ports, misconfigured databases (MongoDB, Elasticsearch), expired SSL/TLS certificates, and exposed administrative interfaces.
GreyNoise
Scan Intelligence & Noise Filtering
Distinguishes between benign internet background noise (mass scanners, research crawlers) and targeted adversary reconnaissance aimed at vendor infrastructure.
BuiltWith
Technology Profiler & Stack Registry
Deep fingerprints the technologies, frameworks, CMS, and third-party JS scripts running on vendor web properties to automatically populate your Technology Register.
MXToolbox
Email Security & Domain Health
Monitors vendor DNS and email security postures in real time, validating SPF records, DKIM cryptographic signatures, DMARC policies, and DNSBL blacklist status.
Auditor-Ready Governance & Automated Planning
Eliminate compliance scramble with pre-scheduled audit cadences, comprehensive standard crosswalks, and one-click Auditor Pack evidence compilation.
Audit Planner & Lifecycle Engine
AUTOMATED CADENCE CONTROL
Keep all vendor reviews on schedule based on customized risk thresholds. High-criticality tier-1 vendors trigger annual deep-dive audits, while continuous OSINT monitors changes between review cycles.
Compliance & Auditors Pack
INSTANT AUDITOR DELIVERABLES
Pre-built cross-mapping allows you to answer external auditors with complete confidence. Export stamped Auditor Packs containing signed questionnaires, SOC 2 bridge letters, and risk mitigation records.
Join the December 2026 Early Access
Secure priority onboarding for your security and risk management teams when CompliScan TPRM launches this December.
Thank you! You are on the priority list for our planned December 2026 launch. The CompliScan team will share private access and technical onboarding materials soon.